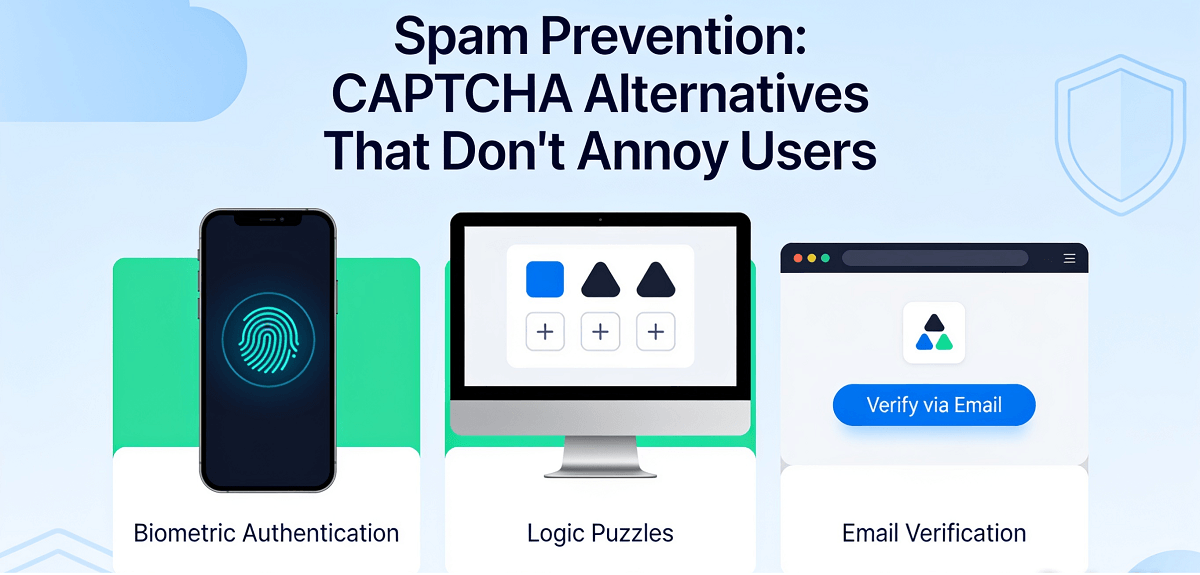
If you run a business website in Singapore, you have probably dealt with spam form submissions. Perhaps your contact form is flooded with gibberish messages, fake enquiries, or promotional garbage that has nothing to do with your business. The traditional solution has been CAPTCHA those those annoying puzzles where you click all the images with traffic lights, or type squiggly letters that you can barely read. While CAPTCHAs do block some spam, they also create friction for real human visitors. Every extra step you ask a genuine customer to take is a potential customer lost. Studies consistently show that complicated CAPTCHAs increase form abandonment rates. The good news is that there are now better, smarter ways to stop spam without punishing the people actually trying to reach you. In this guide, we will walk you through several CAPTCHA alternatives, explain how each one works, and show you exactly how to set them up on your Singapore business website.
Why Traditional CAPTCHA Frustrates Real Visitors
Before we dive into the alternatives, it helps to understand why CAPTCHAs have become such a problem for business owners. A CAPTCHA is fundamentally a test designed to distinguish humans from computers. The problem is that many of these tests are difficult for actual humans too. Elderly visitors may struggle with distorted text. Someone using a phone may find it nearly impossible to select the right image tiles. People in a hurry will simply abandon the form and take their business elsewhere. In Singapore, where mobile commerce and quick enquiries are the norm, you cannot afford to add unnecessary barriers to your contact form. Beyond usability, CAPTCHAs also slow down the user experience. Every second of load time matters. A study by Google found that a 100-millisecond delay in load time can reduce conversions by up to 7 percent. When a CAPTCHA adds three or four seconds plus cognitive effort, you are asking too much. The solution is not to remove spam protection entirely. It is to use smarter methods that do not impact genuine visitors.
Honey Pot Fields: The Invisible Spam Blocker
One of the simplest and most effective CAPTCHA alternatives is called a honey pot field. The concept is clever. You add a form field that is visible to bots but hidden from human users. Spambots automatically fill in every field they see, including fields that real humans would never touch. When your website detects that a hidden field has been filled in, it knows the submission came from a bot, not a person, and it blocks or discards the submission. Here is how to set it up. First, open your website form in edit mode. This could be a WordPress contact form, a Shopify form, or any HTML form you have built. Add a new text input field to your form. Give the field a name that sounds attractive to bots, such as "website", "url", or "email2". Bots tend to fill in fields that look like website URLs or second email fields. Now you need to hide this field from human visitors. The best way is to use CSS to position the field off-screen. Use a style like position: absolute; left: -9999px; or display: none;. Search engines and screen readers will also ignore a field with display: none;, so this is clean for accessibility. Some developers prefer to use a very small one-pixel field with the same color as the background, positioned off to the side. Both approaches work. Next, add a small JavaScript snippet or server-side check. When the form is submitted, check if that hidden field has any value. If it does, reject the submission silently. Do not show an error message to the bot because that gives it information. Just discard it or return a success message so the bot thinks it succeeded. The entire process is invisible to your real visitors. They never see the field and never know it exists. Meanwhile, most basic spam bots will fill it in and get blocked automatically. This method catches a huge percentage of automated spam without any user friction at all.
Time-Based Detection: Catching Slow Humans vs Fast Bots
Another powerful technique is time-based spam detection. Bots fill out forms extremely fast, often in just one or two seconds. Real humans take longer. They read the labels, think about what they want to say, type their message, and then click submit. A human is unlikely to submit a contact form in under three seconds unless they are a robot. To use this method, add a timestamp field to your form when it loads. Record the current time in milliseconds using JavaScript and store it in a hidden form field. You can do this with a simple script that runs when the page finishes loading. When the form is submitted, compare the submission time against the load time. If less than three seconds have passed, the submission is almost certainly from a bot and should be blocked. You can adjust this threshold based on your own testing. Some forms use four seconds as the cutoff. Others use two. The right number depends on how long your form is and how simple or complex your questions are. You should also account for faster internet connections. In Singapore, where fibre broadband is widespread, even real humans can fill out short forms quite quickly. A minimum of two seconds is usually safe. Any submission arriving in one second or less is almost certainly automated. This method is completely invisible to users and requires no extra clicks or puzzles. It is one of the most elegant spam prevention techniques because it works passively.
Using Smart Rate Limiting to Stop Bot Bursts
Rate limiting is a technique that restricts how many times a specific user or IP address can submit a form within a given time window. Bots are programmatic. They can submit dozens or hundreds of forms in minutes. A real human visitor is unlikely to submit more than two or three enquiries in an hour. By setting a reasonable limit, you can slow down spam attacks without affecting legitimate submissions at all. To implement rate limiting, you need to track submissions by IP address. Most web hosting panels in Singapore offer basic rate limiting through their firewall or security settings. If you are using WordPress, plugins like Wordfence include built-in rate limiting that you can configure from the plugin settings panel. Look for options to limit login attempts, contact form submissions, or comment posting. Set the limit to something reasonable, such as five submissions per hour from the same IP address. If you exceed that, the system can temporarily block that IP or show a temporary error message. For more advanced rate limiting, you can use services like Cloudflare. Cloudflare offers a free tier that includes rate limiting rules. You can set rules like "if more than 10 requests per minute come from a single IP, challenge or block them". This is particularly useful if your website is getting attacked from overseas botnets. Singapore businesses that have experienced sudden traffic spikes from unfamiliar geographies often find Cloudflare rate limiting to be an effective first line of defence. Best of all, it does not require any code changes on your part.
Implementing Google reCAPTCHA v3: Invisible Protection
If you still want a Google-powered solution but want to avoid the user friction of traditional CAPTCHA, Google reCAPTCHA v3 is the answer. Unlike earlier versions that required users to solve puzzles or click images, reCAPTCHA v3 runs entirely in the background. It analyses hundreds of signals about how the user is interacting with your page, including their mouse movements, scrolling behaviour, and typing patterns. It then assigns a score from 0.0 to 1.0. Scores closer to 1.0 indicate a likely human. Scores closer to 0.0 suggest a bot. You can set threshold rules in your website code. When someone with a low score tries to submit a form, you can block them, show an additional verification step, or flag the submission for review. Here is how to set it up. First, go to the Google reCAPTCHA admin console at https://www.google.com/recaptcha/admin. Sign in with your Google account. Click the "plus" button to register a new site. Enter your website domain name. Select reCAPTCHA v3 as the type. Accept the terms of service and click Submit. Google will give you two keys: a site key and a secret key. Copy the site key. Now go to your WordPress plugin settings if you are using a plugin like Contact Form 7, Gravity Forms, or WPForms. Look for the reCAPTCHA settings area and paste your site key. If you are using a custom HTML form, you will need to add the reCAPTCHA script to your page head section with your site key. Then add a invisible div element where you want the reCAPTCHA badge to appear. Your form plugin or custom code will automatically communicate with Google's servers and evaluate each submission. The process is seamless for the user. They see nothing except perhaps a small reCAPTCHA badge in the corner of your page. No puzzles, no frustration, just smooth protection that works in the background.
Cloudflare Turnstile: Free and User-Friendly
Cloudflare has launched its own CAPTCHA alternative called Turnstile, and it is worth considering for Singapore business websites. Turnstile is completely free and designed to replace traditional CAPTCHA without the user friction. It works similarly to reCAPTCHA v3 in that it runs invisible checks in the background. However, Turnstile offers a few advantages. It does not require you to load Google's JavaScript libraries, which can improve page load speed. It also offers multiple widget modes. The "managed" mode runs silent checks and only shows a challenge if it detects suspicious behaviour. The "non-interactive" mode runs checks without ever showing anything to the user. The "invisible" mode is similar but uses a full invisible challenge when needed. To get started with Turnstile, log in to your Cloudflare dashboard. If you do not already have a Cloudflare account, you can create one for free and add your domain. Once your domain is on Cloudflare, go to the Turnstile section in the Security tab. Click Add widget. Give it a name and select your preferred widget mode. Add your domain and any subdomains you want to cover. Cloudflare will give you a site key and a secret key. Paste the site key into your website forms using Cloudflare's provided code snippet or through your CMS plugin settings. Many popular WordPress forms plugins now have native Turnstile support. If your plugin does not support it directly, you can add the Turnstile JavaScript embed code to your page manually. The result is a frictionless experience for your visitors while Cloudflare handles the spam detection silently in the cloud.
Akismet: Built-in Spam Filtering for WordPress
If your Singapore business website runs on WordPress, Akismet is one of the easiest spam filtering tools to set up and forget about. Akismet was originally built for WordPress comment spam but it works equally well for contact form submissions. It works by checking all submissions against a global database of known spam patterns. When a submission comes in, Akismet analyses it and returns a spam score. If it flags the message as spam, you can have it automatically discarded or sent to your spam folder for review. To activate Akismet, install the Akismet plugin from the WordPress plugin directory if it is not already installed. Then go to the Akismet settings page and get an API key. You can start with the free plan for personal or charity websites. For business websites, paid plans start at a reasonable monthly fee. Once the API key is entered and activated, Akismet starts filtering automatically. You do not need to configure complex rules. The system learns over time as it processes more submissions. You can also review the spam queue periodically to make sure legitimate enquiries are not being caught. This low-maintenance approach is ideal for busy business owners who want effective spam protection without managing complex settings on a daily basis.
Double Opt-In for Email Forms: Killing Two Birds With One Stone
If your form collects email addresses, a double opt-in verification process is an excellent spam prevention measure that also improves your email list quality. The process works like this. A visitor fills in your form and submits their email address. Your website automatically sends them a confirmation email with a unique clickable link. They must click that link to confirm they are real and genuinely want to receive your communications. Bots submitting forms typically use fake or random email addresses. Those addresses either do not exist or the bot does not have access to them, so the bot cannot click the confirmation link. The result is that spam submissions are filtered out automatically and you end up with only verified, real email addresses in your database. To set this up, you need an email marketing service that supports double opt-in. Mailchimp, ConvertKit, and Sendinblue all support this feature natively. When you create a signup form in these tools, there is a setting to require subscribers to confirm their email address. Enable that setting and all future form submissions will go through the verification process. This approach is particularly popular for newsletter signups and enquiry forms where email follow-up is expected. It protects you from spam and improves your email deliverability at the same time.
IP Blocklisting: Stop Repeat Offenders
Sometimes a specific IP address or range of IP addresses will bombard your forms with spam. This can happen when a spammer targets your business specifically or when a previously clean IP address gets compromised and added to a botnet. Most web hosting providers and security plugins allow you to block specific IP addresses manually. When you notice spam submissions coming from the same IP repeatedly, add that IP to your blocklist. In WordPress, you can do this through Wordfence or Sucuri security plugins. In your Cloudflare dashboard, you can block IPs directly from the security settings panel. For more automated blocklisting, consider using a service that maintains real-time blocklists of known spam sources. Projects like Spamhaus and Barracuda maintain lists of IP addresses associated with spam campaigns. Many security plugins can automatically check submissions against these blocklists and reject matches. This approach is reactive rather than proactive, meaning you add IPs after you see spam from them. But combined with other methods on this list, it forms a useful additional layer of protection.
Combining Multiple Methods: A Layered Defence
No single spam prevention method is perfect. Bots evolve. New techniques appear. That is why the most effective approach is to combine multiple methods in layers. Think of it like a security system for your home. A lock on your door is good, but combining a lock with a security camera, motion sensors, and an alarm is much stronger. For your website forms, consider layering honey pot fields with time-based detection and a reCAPTCHA v3 or Turnstile integration. This way, if one method misses a sophisticated bot, another layer catches it. The good news is that these layered methods do not add visible friction for your real visitors. Honey pot fields and time detection are completely invisible. reCAPTCHA v3 and Turnstile show nothing to most users. Only in rare cases where the system suspects bot activity would any additional challenge appear. Your genuine Singapore customers will never notice the protection is there. Meanwhile, spam submissions will drop dramatically, freeing up your time to focus on real enquiries and growing your business.
Spam does not have to be a daily frustration. With the right tools and a few smart configuration steps, you can protect your forms without making your website harder to use. Start with the methods that require the least setup, such as honey pot fields and time-based detection. These cost nothing and take only a few minutes to implement. Then add a service like reCAPTCHA v3 or Turnstile for the remaining automated protection. Your website visitors will thank you, and you will enjoy a cleaner, more manageable inbox.
If you still need help, feel free to contact us at https://webcare.sg/contact for a free website health check.